What it covers
The scans look at what the merge request adds or changes, for its head commit, and each is a control of the policy: off, reported or enforced.
Secrets
Added lines and the names of added or changed files, and by default the title, the description and commit messages, are scanned for secrets. An extra rule set for connection strings, password assignments, credentials in URLs and CI tokens can be turned on.
Read the docsVulnerable dependencies
Changed manifests and lockfiles are compared with the target branch and the new versions are looked up in OSV.dev. Vulnerabilities exploited in the wild (CISA KEV) and their exploitation likelihood (FIRST EPSS) are marked.
Read the docs15 package ecosystems
Go, npm, PyPI, Maven, crates.io, RubyGems, NuGet, Packagist, Pub, SwiftPM, CocoaPods, Hex, Hackage, Conan and CRAN manifests are read; vulnerabilities are looked up for all but CocoaPods, which OSV.dev does not cover.
Read the docsLicenses
The SPDX licenses of new dependencies come from deps.dev, for Go, npm, PyPI, Maven, crates.io, NuGet and RubyGems, and are checked against the company's denied and allowed lists.
Read the docsPackage health
Versions published only days ago, or deprecated by their registry, are findings.
Read the docsDependency sources
New and changed lockfile entries are checked for where they come from: registries that are not allowed (dependency confusion), git, URL and local path dependencies, pip index options, and manifests changed without their lockfile.
Read the docsCI configuration
Changed GitHub Actions workflows and GitLab CI configuration are checked for script injection, untrusted checkouts, unpinned actions, includes and images, debug logging and caches shared with unprotected branches, each with a severity.
Read the docsContainer images
The container images a change starts referring to (Dockerfile FROM lines, Kubernetes manifests, Helm values and Compose files) are scanned for packages with known vulnerabilities; images the target branch already uses are not scanned again.
Read the docsInfrastructure
Misconfigurations a change introduces in Terraform, Kubernetes manifests, Helm charts, Dockerfiles, CloudFormation and Azure Resource Manager templates are found; problems the target branch already has are not counted.
Read the docsSigned commits
Commits without a signature the VCS verified can hold the change; bots and service accounts that cannot sign can be exempted.
Read the docs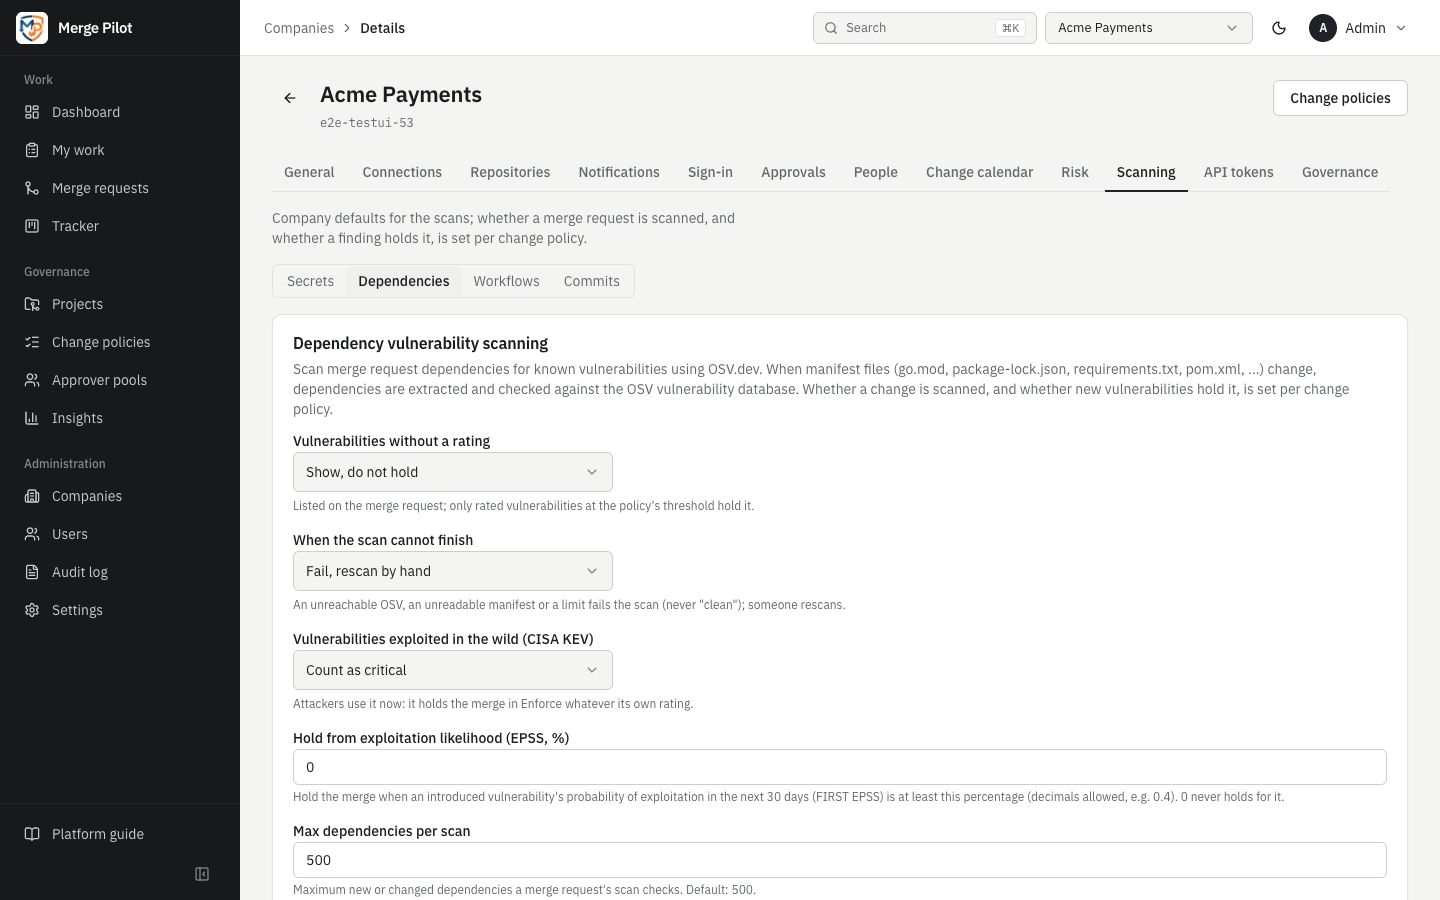
See it on your own repositories
Ask for a demo on your own GitLab or GitHub repositories.